PSIRT & CSIRT
UfiSpace Vulnerability Reporting
At UfiSpace, we recognize the critical importance of open networking and carrier-grade infrastructure security to the global telecommunications ecosystem. We are committed to securing our hardware, firmware (NOS), and software products, as well as proactively safeguarding our enterprise operational architecture. The PSIRT and CSIRT teams are dedicated to receiving, verifying, and addressing all security advisories and incident reports regarding UfiSpace whitebox switches, routers, and digital services. Through close collaboration with our customers, telecom partners, and the cybersecurity research community, we continuously uphold the operational security and security resilience of open communications networks.
Dedicated Reporting Channels
If you discover a potential security vulnerability or incident involving UfiSpace products or systems, please refer to the appropriate reporting channel below based on the issue type
Product Security Incident Response Team (PSIRT)
PSIRT is responsible for addressing security vulnerabilities in UfiSpace's commercially available whitebox switches, routers, hardware, and software/firmware products, ensuring the operational security of our customers' network infrastructure.
Handling vulnerability reports, assessing severity levels based on the CVSS standard, coordinating with engineering teams to develop security patches or workarounds, and publishing official Security Advisories.
Product Security Incident Response Team (PSIRT)
Security vulnerabilities related to UfiSpace hardware devices, system firmware, NOS software, or telecom product lines.
Email:psirt@ufispace.com
Computer Security Incident Response Team (CSIRT)
Security incidents related to UfiSpace's corporate website, online customer service portal, internal IT systems, or data privacy.
Email:csirt@ufispace.com
Computer Security Incident Response Team (CSIRT)
CSIRT is dedicated to maintaining the security of UfiSpace's enterprise network, information systems, digital assets, and internal operational environments, protecting against social engineering and cyber threats.
Monitoring threats to operational systems, executing incident response, handling brand impersonation and phishing incidents, and ensuring compliance with international cybersecurity standards.
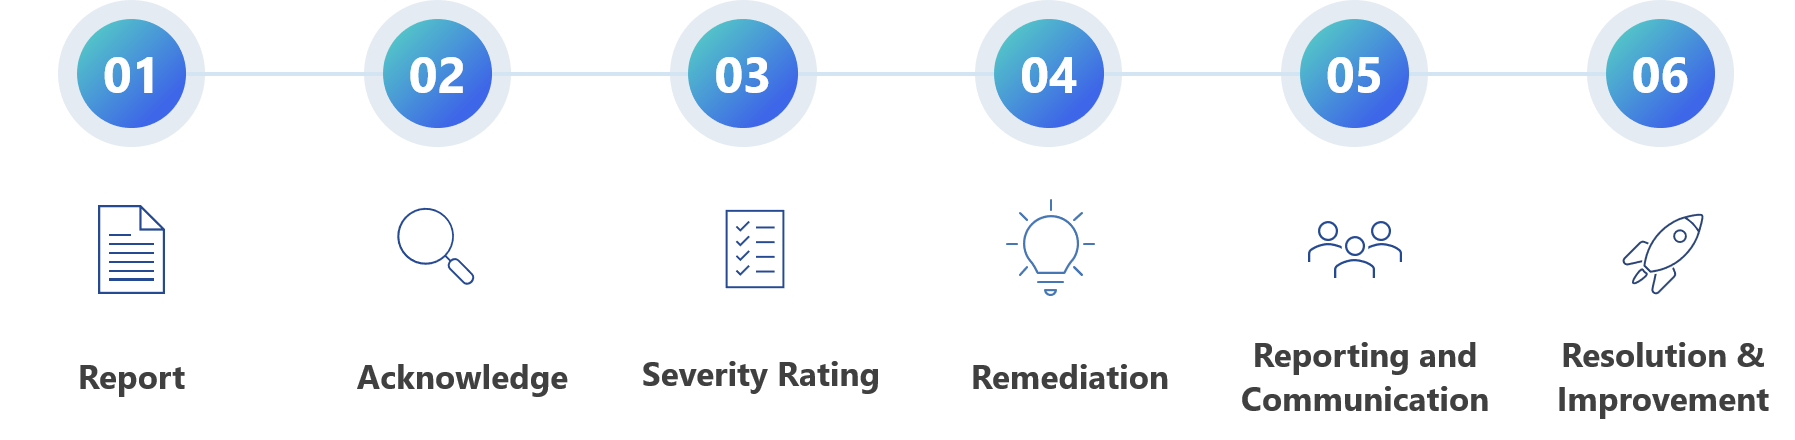
Vulnerability Response Process